 QRCoder
QR code safety
Check a QR Code Link Before You Open It
A QR code is just a link you cannot read. That is what makes "quishing" — QR phishing — work: a sticker over a parking meter, a code in an email, a fake menu on a café table. The defence is simple: read the link before you open it.
Where malicious QR codes show up
- Parking meters and EV chargers — a sticker placed over the real code leads to a fake payment page. The FBI has warned about tampered QR codes being used to steal payment details.
- Emails and letters — "scan to verify your account" or "scan to reschedule delivery". Legitimate organisations rarely need you to scan a code to log in.
- Restaurant tables and posters — a replacement code can send you to a lookalike ordering page.
- Parcel notices — a card in the mailbox asking you to scan to "claim" a package you did not expect.
Read the link in four checks
- Find the real domain. The domain is the part right before the first single slash, read from the right: in
pay.cityparking.example.com/meter, the site isexample.com, notcityparking. Attackers put a trusted name on the left and their own domain on the right. - Look for lookalikes. Swapped letters (
paypa1), extra words (citypark-payments), or unusual endings (.top,.xyz) on a site that should be official. - Be wary of shorteners. A
bit.ly-style link hides the destination. For payments or logins, don't open it — go to the official site or app yourself. - Check that it fits the context. A parking code should lead to the city or the operator named on the meter; a restaurant menu should not ask for card details or a login.
How QRCoder helps
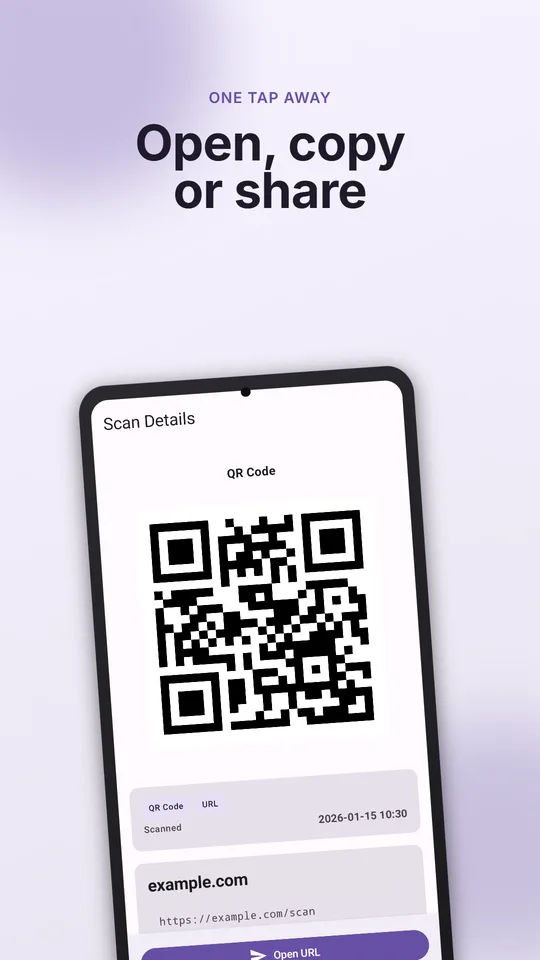
QRCoder never opens a link automatically. After a scan it shows the domain, the full address and local warnings about suspicious links, so you can make the four checks above before tapping Open. The check happens on your phone — scanning does not send the link to a server. For Wi-Fi, contacts and calendar events, the app shows the fields clearly and hands off to Android's own confirmation screen, so nothing is joined or saved without your approval.
Physical checks for public codes
- Run a finger over the code. A sticker on top of printed signage is a red flag.
- Compare with the operator's name or website printed elsewhere on the sign.
- If there is an official app or a card terminal, use that instead of the code.
Rule of thumb: if a QR code leads to a page asking for a password, card number or one-time code, close it and go to the service directly by typing its address or using its official app.
If you already opened a bad link
- Do not enter anything else. Close the page.
- If you entered card details, contact your bank immediately and ask for the card to be blocked.
- If you entered a password, change it on the real site and on any site where you reused it, and turn on two-factor authentication.
- Report the tampered code to the business or the parking operator. In the US you can also report fraud to the FTC at ReportFraud.ftc.gov.
Frequently asked questions
Can scanning a QR code hack my phone?
Scanning itself only decodes text. The risk comes from what you do next: opening a malicious page, entering details, or installing an app. Reading the link before opening it removes most of that risk.
Does QRCoder open links automatically?
No. It shows the domain, the full address and local warnings about suspicious links first, and only opens the link when you tap Open.
How do I know if a parking meter QR code is fake?
Check whether the code is a sticker placed over the sign, and whether the link's domain matches the operator named on the meter. When in doubt, pay through the operator's official app or the meter itself.
Sources and further reading
How this article was created
This article was drafted with the help of artificial intelligence and edited against the app's published feature list. The independent developer is responsible for publication and accepts correction reports. Verify health, safety, legal, financial and official requirements with a primary source or qualified professional.
Questions and corrections: brightwaveapp@gmail.com. Legal and privacy information.